Since 11 September 2026, manufacturers of products with digital elements have been required to report actively exploited vulnerabilities and severe security incidents under the EU Cyber Resilience Act.
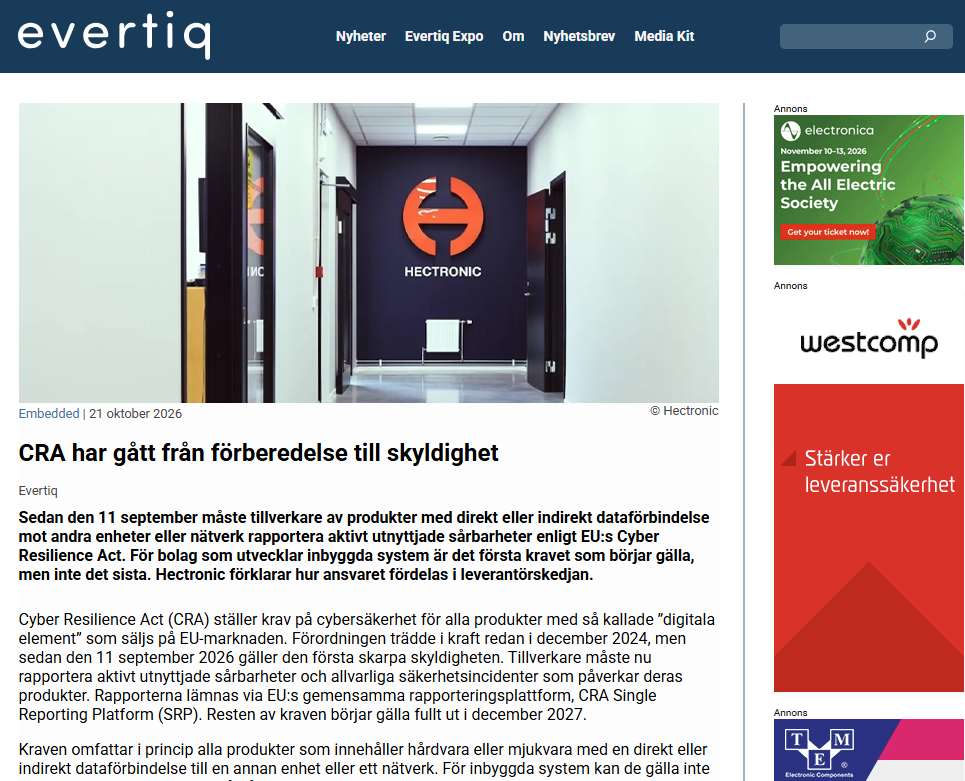
In a recent article published by Swedish electronics industry publication Evertiq, Hectronic discusses what these requirements mean for embedded system development, with a particular focus on cybersecurity responsibilities throughout the supply chain.
Magnus Wingmark, Head of Business Department at Hectronic, highlights the importance of understanding how responsibilities extend beyond product delivery, including vulnerability management, security updates and long-term maintenance.
Read the full article on Evertiq (in Swedish).
For a more detailed overview of the CRA and its implications for embedded systems, visit our Cyber Resilience Act for Embedded Systems page.